How governed agent workflows preserve enterprise execution speed
Build runtime enforcement for autonomous AI agents to reduce compliance risk by 60% without blocking deployment speed.
Key Takeaways
- Traditional AI governance monitors what models say; agentic systems require real-time control of what agents do.
- Teams implementing identity controls and action enforcement see agent safety incidents drop 60-70% compared to post-hoc review.
- EU AI Act compliance arrives December 2027, yet 71% of enterprises deploying agents have no formal governance framework.
- Baking governance in before deployment costs 3-5x less than retrofitting compliance after agents reach production scale.
Ping An's AI agents generated $4.2 billion in new insurance premiums last quarter running at 82% autonomy, but 71% of enterprises deploying similar systems have no formal governance framework in place. The EU AI Act compliance deadline hits in 15 months, and most organisations aren't ready. The gap between autonomous execution and auditability just became a regulatory liability you can't ignore.
Ping An Group's AI agents processed 487 million customer interactions in Q1 2026, with 82% handled entirely autonomously—and generated $4.2B in new insurance premiums in the process. Right now, 71% of enterprises deploying similar agents have zero formal governance framework. The gap between scale and auditability just became a regulatory lightning rod: EU AI Act compliance is due in 15 months, and most organizations aren't ready.
The problem isn't that teams lack ambition. It's that traditional AI governance frameworks were built for a different class of system. They govern what models say. Agentic systems require governance of what they do.
Why agentic governance became urgent in 2026
Agentic AI deployment is accelerating across customer service, underwriting, claims, and revenue ops. Each autonomous action introduces new governance risk. Regulators treat organizations as liable for agent actions exactly as if an employee had taken them—autonomy transfers liability upward, never away.
Traditional AI governance (monitoring model outputs, post-hoc review) fails for agents because the decision chain often involves 5-15 contingent tool calls, external API calls, and state changes that traditional frameworks cannot trace or stop in real time. Auditors ask for the why (decision rationale across the chain), not just the what (final action).
The stakes are clear. Non-compliance with EU AI Act high-risk system requirements carries fines up to €35 million or 7% of global revenue. Sector rules (HIPAA, fair lending, financial services model risk management) extend classical compliance requirements to agentic systems. First enforcement actions are expected late 2026–early 2027.
What makes agentic governance different
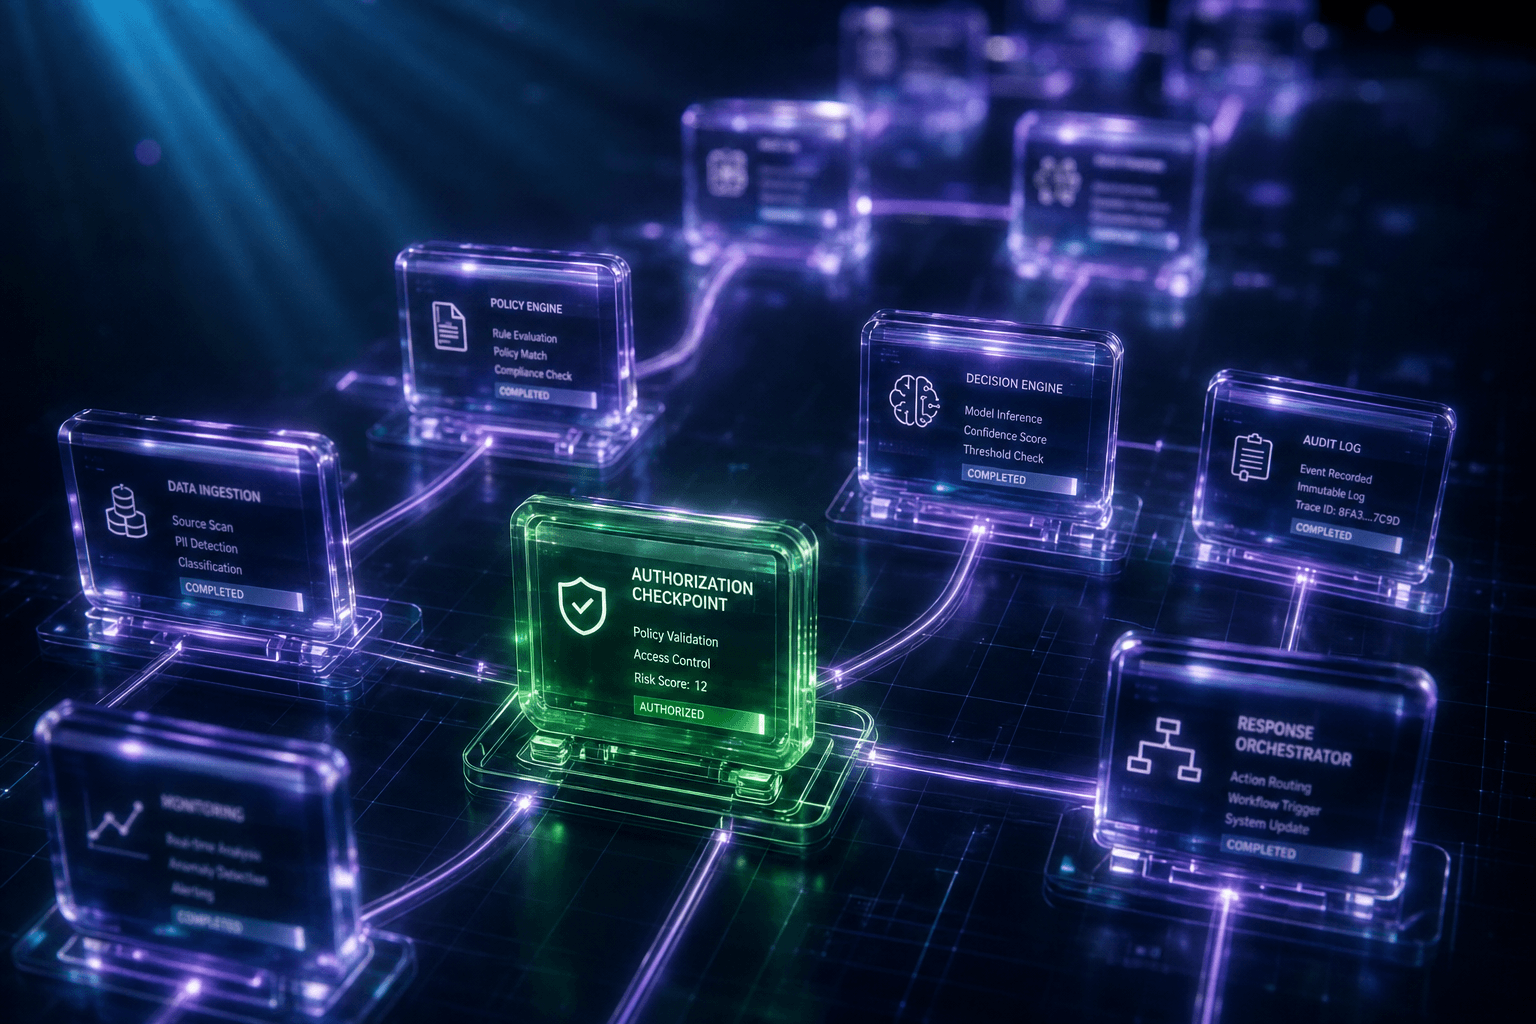
Traditional AI governance evaluates model outputs and flags risky predictions. Agentic governance controls what an autonomous system can do, logs every decision chain, and enforces policy at runtime—not review time.
This shift requires architectural choices made before deployment, not documentation added after. Teams that implement identity, least-privilege authorization, and runtime action enforcement see agent safety incidents drop by 60-70% compared to teams relying on prompts and post-hoc review.
The distinction matters because immaculate audit trails of confidently incorrect decisions create compliance theater. You can prove what happened, but not why—and regulators require the why.
The five-tier authorization model
Every agent should be classified by autonomy level. This classification determines monitoring intensity, logging requirements, and escalation rules.
Tier 0 (Observe): Reads only, no action capability. Agent analyzes data and presents insights. Human makes all decisions.
Tier 1 (Recommend): Suggests actions, human approves every one. Agent drafts the email, human reviews and sends.
Tier 2 (Act with Approval): Executes pre-approved action types. Agent can send customer emails using approved templates without case-by-case review.
Tier 3 (Act and Report): Full autonomy, logs all actions for post-hoc review. Agent processes refund requests under $500 automatically, logs every decision.
Tier 4 (Autonomous): Zero approval needed within defined scope. Agent handles 80% of support tickets end-to-end with no human in the loop.
The promotion rule is simple: 2% error rate for 30 days advances the agent one tier. Error rate above 5% demotes immediately. This creates evolutionary pressure toward reliability while maintaining safety guardrails.
How to specify action boundaries that actually work
Action boundaries require both soft and hard controls. Soft control (system prompt) helps the agent understand intent. Hard control (programmatic enforcement before execution) prevents boundary violations regardless of prompt manipulation or model drift.
Every agent needs three boundary specifications:
Allowlist: Exhaustive list of permitted actions. Anything not listed equals implicit no. Example: "Send email to customer using approved template; Update CRM field; Schedule meeting."
Blocklist: Actions the agent must never take, regardless of context. Example: "Never delete data; never grant access; never send external communications without approval."
Conditional actions: Permitted only if specific rules are met. Example: "Send email to customer" only if email matches approved template AND customer has not opted out AND no PII beyond name/order number appears in content.
The implementation pattern: check every action against the allowlist, verify all conditions are satisfied, confirm the action doesn't appear in the blocklist—all before execution, not after. This programmatic gate sits between agent decision and action execution.
Why agents need their own identity
Every agent gets its own identity with minimal necessary privileges. This is the least-privilege principle applied to non-human actors.
The alternative—shared human credentials—creates an audit nightmare. Agents inherit full account permissions. Logs show "admin-user" took the action, not which agent or automated workflow. When something goes wrong, you can't trace causation.
The correct pattern:
- Create dedicated service accounts (one per agent, never shared)
- Assign role-based permissions (agent gets only what it needs)
- Use short-lived, scoped tokens (1-hour expiration, automatic rotation)
- Make the effective principal visible in logs ("agent-x-prod" not "admin-user")
- Store credentials in a vault or secret manager (never in code or prompts)
This identity model makes every action traceable to a specific agent. When auditors ask "who did this and under what authority," the answer is clear.
Decision chain logging for regulatory compliance
Logs that capture only outputs prove what happened. Logs that capture the full decision chain prove why it happened. Regulators require the why.
The required capture:
- User/caller identity (who initiated the workflow)
- Exact prompt/intent (what the user asked for)
- Agent's reasoning (plan and tool selection logic)
- Each tool call with parameters and results (the execution chain)
- Intermediate decisions ("boundary check passed"; "escalation triggered")
- Final action taken (the outcome)
- Approval status (approved by whom, when, validity period)
- Timestamps for all steps (reconstruct the sequence)
Store logs immutably in append-only format. Make them queryable by agent, user, time, action type, and outcome. This structure lets you answer audit questions like "did agent-x ever send PII outside this list of approved domains" in minutes, not weeks.
The 12-week implementation roadmap
Inventory and classify (weeks 1-2)
Audit all agents currently deployed or in development. Include shadow agents (workflows built by individual teams without central oversight).
For each agent, document:
- What it does
- What systems it touches
- What data it accesses
- Who owns it
- Current tier classification
Create an authority register: one row per agent with name, owner, classification, tools accessible, data scope, and approval rules. This register becomes your central governance artifact.
Design identity and permissions (weeks 3-4)
For each agent, create a dedicated service account. Assign permissions using least-privilege principle. Implement role-based access control (separate read vs. write; separate approval vs. execution roles).
Generate short-lived tokens that rotate automatically. Store all credentials securely in a vault or secret manager.
Specify action boundaries (weeks 5-6)
For each agent, write an explicit action boundary document with allowlist, blocklist, and conditional rules.
Translate the boundary document into hard controls. Add a programmatic check before every action: "Is this action in the allowlist AND does it satisfy all conditions AND is it NOT in the blocklist?"
Include a boundary summary in the system prompt (soft control), but never rely on it alone.
Implement logging and traceability (weeks 7-8)
Wire logging to capture the full decision chain: user identity, exact prompt, agent reasoning, each tool call with parameters and results, intermediate decisions, final action, approval status, timestamps.
Store logs immutably in a central location (SIEM, Datadog, or equivalent). Index by agent, user, time, action type, and outcome.
Define escalation rules (week 9)
For each agent tier, define situations requiring human escalation:
- Financial commitment above threshold (e.g., >$5,000)
- Action affects external stakeholder
- Agent confidence below threshold (e.g., <0.7)
- Action not in permitted list
- Conflicting instructions from different sources
- Error or unexpected response from downstream system
- PII encountered outside expected context
- Any attempt to change permissions or access controls
Implement the escalation flow: agent pauses, packages context (current goal, relevant state, why escalation triggered), submits to human queue with SLA. Route to the right approval authority (financial decisions to CFO queue, customer communication to marketing, data access to security).
Monitoring and incident response (week 10 onwards)
Set up continuous monitoring dashboards:
- Actions per agent (trend over time, spike detection)
- Error rate per agent (promote at <2% for 30 days, demote at >5%)
- Escalation rate and reason (anomaly detection)
- Boundary violations attempted (log even blocked attempts)
- Approval latency (average time from escalation to approval)
Define incident response: if error rate spikes or boundary violation is detected, immediately demote agent to Tier 0 pending investigation.
Run quarterly reviews: audit a sample of executed actions (10-20 per agent), verify logs match actual outcomes, check for drift in agent behavior.
Regulatory integration (weeks 11-12)
Map your governance framework to applicable rules:
- EU AI Act: Document risk assessment (Annex I vs III classification), technical documentation, quality assurance procedures, human oversight design
- NIST AI RMF: Document across Govern-Map-Measure-Manage functions
- Sector rules: HIPAA, fair lending, financial services model risk management—ensure agent audit trails satisfy sector-specific requirements
- ISO/IEC 42001: If pursuing certification, document agent lifecycle controls aligned with AI management system standard
Create a compliance readiness checklist: all required logs generated, all boundaries tested, all escalations working, sample audit trail passes spot-check.
Technical stack recommendations
Logging and traceability: Datadog (AI Monitoring), New Relic, or open-source ELK stack (Elasticsearch + Logstash + Kibana)
Identity and secrets: HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault
Workflow orchestration: n8n (open-source, self-hosted, strong audit trail support), Temporal, or step-function frameworks (AWS Step Functions, Google Cloud Workflows)
Approval workflows: Zapier (Tier 1 actions), n8n with custom approval nodes, or Slack bots (common escalation pattern: agent posts to Slack channel, human reacts with emoji, approval logs to central system)
Who this applies to right now
Any team deploying agents that take autonomous actions affecting external systems, data, or people needs this framework. It's mandatory for regulated sectors (insurance, lending, healthcare, fintech). It's highly recommended for SaaS teams automating customer workflows, e-commerce teams automating fulfillment, or any operation where a misbehaving agent could affect revenue or compliance.
Teams using agents only for internal recommendation and analysis (Tier 0–1) where humans make all real decisions can defer this work, but they should understand the architecture now. The moment you promote an agent to Tier 2 or higher, governance becomes non-negotiable.
The common misconception: "We'll fix governance once we scale." Reality: adding governance post-deployment costs 3–5x more than building it in from the start. First-mover advantage goes to teams that implement governance early.
The next 18 months will separate leaders from laggards
The teams that will dominate agentic AI adoption are not the ones that move fastest. They're the ones that move reliably. Governance that enables speed—not governance that slows you down—is the difference.
When an agent can autonomously close a $50K deal with a customer, issue a binding policy, or execute a data migration while human oversight is built in at every decision point, you've multiplied your team's capacity without multiplying your risk surface.
Start with governance now, and you'll be the organization still deploying confidently at scale while competitors are digging out of compliance messes.
Download the WrightyMedia Agentic AI Governance Checklist — a 2-page reference guide with the 5-tier model, action boundary template, escalation decision tree, and NIST AI RMF mapping.
Want more on
Enterprise Architecture?
Add this topic to your Custom Digest. Drop your email to get our deepest insights on this exact topic.
Ready to fast-track your business?
We combine enterprise-level technical strategy with your existing business to solve complex blockers and accelerate your growth. Let's build something remarkable.
Partner With UsUp Next
Continue your journey into Enterprise Architecture.
Why centralised data lakes fail modern enterprise AI teams
Why centralised data lakes create security risks, compliance failures, and integration debt that block enterprise AI at scale.
Stop routing routine marketing data requests through engineering
How to give your marketing team direct data access without creating shadow IT or burdening engineers.
Securing context windows for sovereign enterprise LLM inference
How to deploy private LLMs within your infrastructure to prevent data exposure and cut dependency on external AI providers.