The governance gap why 40% of enterprise AI agent pilots will be
Why most enterprise AI agent pilots fail governance review and how to architect approval workflows that pass regulatory audit.
Key Takeaways
- Only 10% of companies have scaled AI agents to production because governance architecture comes too late.
- The EU AI Act starts enforcement in December 2027 with €15M fines for non-compliant autonomous systems.
- Production teams invest 40-50% of deployment effort in approval workflows, audit trails, and access controls.
- Graduated autonomy deploys agents in constrained mode first, then expands permissions based on 30-day performance data.
Gartner predicts 40% of enterprise AI agent pilots will be cancelled by end of 2027—not because the technology failed, but because governance infrastructure was never built. The EU AI Act begins enforcement in December 2027 with €15M fines, and only 1 in 10 companies have actually scaled agents into production. The gap isn't capability; it's architecture.
Gartner data from October 2026 reveals an uncomfortable truth: 40% of enterprise AI agent pilots will be canceled by end of 2027. The reason isn't capability. It's governance.
Only 1 in 10 companies have scaled agents into production. The bottleneck isn't prompt engineering or model accuracy—it's the absence of approval workflows, audit trails, and human-in-the-loop architecture. With EU AI Act enforcement beginning December 2027 (€15M fines), the clock is running out.
Why agents fail when they move from read to write
AI agents performing read-only tasks—summarization, data retrieval, reporting—operate in low-risk territory. The moment they write to production systems (invoice processing, supply chain decisions, financial approvals), the risk profile changes completely.
Current state across enterprise:
- Only 5% of organizations achieve 100% traceable AI output
- 50%+ have zero AI governance framework
- 85% want to be "agentic" in three years
- 24% admit their infrastructure can support it
The structural problem: teams are deploying autonomy without answering "Who approved this automated action, and can we prove it to a regulator?"
The cost of retrofitting governance after deployment is high. Security reviews kill most projects. The teams shipping at scale are embedding governance architecture before the first agent executes.
The autonomy-control dilemma
Autonomous systems require governance constraints as architecture-first decisions, not retrofitted audits.
This isn't new to software. Banks handle payment systems this way. Healthcare handles pharmacy workflows this way. Supply chains handle procurement automation this way. What's new is that most enterprise teams building agents have never designed operational systems with automated decision-making authority.
The pattern that works: treat AI agents as software systems first (with operational infrastructure, access controls, and approval workflows embedded from day one) and AI products second.
Teams succeeding in production invest 40-50% of effort in governance scaffolding—not prompt engineering.
Three architectural layers for production agents
Graduated autonomy deployment
Agents should not launch at full autonomy. Production-proven pattern:
- Deploy at conservative autonomy
- Validate performance over 30+ days
- Graduate incrementally based on measured override rates
Example: Invoice processing agent progression
- Week 1-30: "Flag for review" mode (100% human approval)
- Week 31-60: Auto-approve under $5K
- Week 61-90: Auto-approve under $50K with existing vendors
- Week 90+: Full autonomy with human spot-check sampling
This requires architecture supporting multiple autonomy modes, not a single on/off switch.
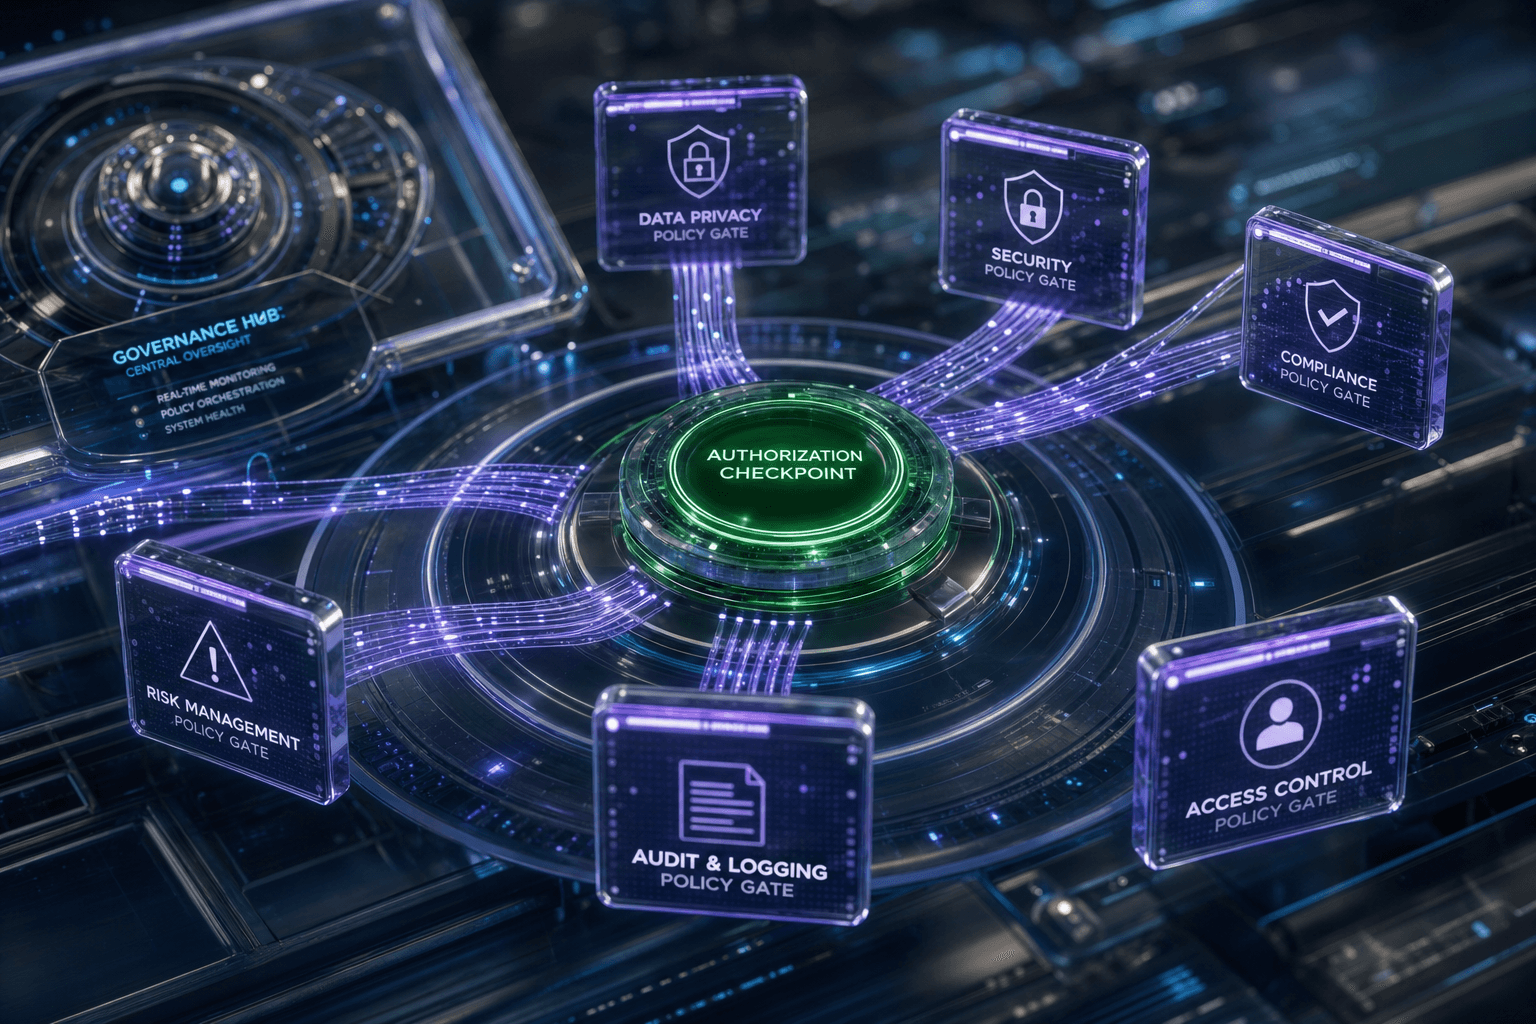
Four governance design patterns
Production deployments typically blend multiple patterns for different action types:
Interrupt and Resume (synchronous approval checkpoint)
- Agent proposes action
- Human receives approval request in real-time
- Agent waits for approval before executing
- Use case: High-risk financial decisions, contract modifications
Human as Tool (agent calls human on uncertainty)
- Agent encounters ambiguous data or edge case
- Agent asks clarifying question via Slack/email
- Human provides context
- Agent continues with new information
- Use case: Data quality issues, vendor classification
Approval Flows (policy-driven automatic routing)
- Agent checks action against predefined policies
- If within policy parameters, executes automatically
- If outside parameters, routes to appropriate approver
- Use case: Tiered spending limits, conditional vendor approvals
Fallback Escalation (async notification with safe default)
- Agent takes conservative action automatically
- Sends notification to human
- Human can override within defined window
- Use case: Low-risk status updates, routine communications
Most teams implement one pattern. That's why they fail at scale.
Immutable audit trails as infrastructure
Every agent decision, approval, override, and execution must be logged with:
- Timestamp
- Actor (human or agent)
- Context (data inputs, reasoning)
- Outcome (action taken, any modifications)
This requires:
- Database design with versioning
- Access control segregation (builder ≠ approver ≠ auditor)
- Versioning of policies themselves
- Read-only audit accounts
Retrofit audit logging is expensive and rarely complete. Security reviews catch this immediately.
Who this applies to (and who IT doesn't)
You need governance architecture if:
- Processing 100+ automation workflows with agent integration
- Deploying agents that write to systems of record (ERP, CRM, financial systems)
- Operating in regulated industries (finance, healthcare, supply chain)
- Embedding agent capabilities as customer-facing B2B SaaS features
You can skip this if:
- Running internal, read-only analytics agents
- Deploying single-function chatbots
- Operating pilot projects with <10 monthly executions
- Building purely informational workflows
Honest assessment: Governance architecture adds 30-40% overhead to agent deployment timelines. Teams underestimate this friction.
The payoff: lower operational risk, faster regulatory approval, and 2-3x faster time-to-value on subsequent agents (because infrastructure is already in place).
Six-phase deployment blueprint
Map and classify (week 1-2)
- Inventory every action your agent will take (read, write, approve, escalate)
- Classify each by risk level:
- Low: read-only operations
- Medium: conditional writes with reversibility
- High: financial decisions, compliance actions, irreversible writes
- Define oversight requirement per action:
- Logging only?
- Asynchronous notification?
- Synchronous approval?
- Document the actor who should approve each action type (finance lead, ops manager, compliance officer)
Choose governance pattern (week 2-3)
For each action class, select the appropriate design pattern:
- High-risk financial decisions → Interrupt and Resume
- Medium-risk supplier changes → Approval Flows (policy-driven routing)
- Low-risk status updates → Fallback Escalation (async Slack notification)
- Uncertainty detection → Human as Tool
Document the rationale. Regulators will ask.
Architect the approval system (week 3-4)
Build approval request data structure:
- Agent proposed action (what it wants to do)
- Reasoning context (why it chose this action)
- Risk classification (rule applied, if policy-driven)
- Requested approver (role, not individual)
Design approval workflow:
- Approval UI (web form, Slack slash command, email reply)
- Routing logic (sync vs. async? escalation if no response in 2 hours?)
- Audit logging trigger (record approval, who approved, timestamp, any modifications)
Implement role segregation:
- Build agent account (read permissions, write within defined boundaries)
- Create approval account (read permissions, write to approval table only)
- Create audit account (read-only access to approval logs, separate database user)
The segregation prevents the team building the agent from approving its own actions.
Define governance kpis (week 4-5)
Most teams only measure accuracy. That's insufficient for production.
Track these metrics:
- Approval latency (P50, P95: time from request to approval)
- Override rate (% of agent proposals rejected by human)
- Policy hit rate (% of actions matching predefined approval policies)
- Audit trail completeness (% of actions with matching log entries)
- Mean time to policy update (when policy changes, how fast deployed?)
These KPIs answer the question regulators will ask: "How do you know your agent is operating within approved boundaries?"
Graduated autonomy pilot (week 5-12)
- Deploy agent in constrained mode: all actions require synchronous approval
- Run 30 days, measure override rate and approval latency
- If override rate <5% and latency <2hrs, graduate to policy-driven approval (no human approval for <$5K)
- Run another 30 days
- If override rate remains <5%, graduate again
- Document each graduation decision for regulatory audit trail
The documentation matters. EU AI Act compliance requires demonstrating that you validated performance before expanding autonomy.
Operational readiness (week 12+)
Deploy agent to production only after passing governance readiness checklist:
- Approval workflow tested with 10+ scenarios
- Audit logs validated for completeness
- Escalation paths documented and tested
- Role segregation verified (builder cannot approve own actions)
- 60+ day pilot KPI dashboard established
- Regulatory compliance document drafted (EU AI Act attestation, if applicable)
Real-world example invoice processing agent
Here's how a mid-market manufacturing company deployed an invoice processing agent with governance architecture:
Autonomy tiers:
- Invoices <$1K: auto-approved (fallback escalation to email if data quality flag)
- Invoices $1K-$10K: auto-approved if vendor is existing + all line items match PO (policy-driven)
- Invoices $10K+: synchronous approval (interrupt and resume)
- Data quality issues: human as tool (agent asks clarifying question via Slack)
Audit trail: All actions logged with vendor name, amount, approver, timestamp, and override status. Logs stored in separate database with read-only access for finance team.
Results after 90 days:
- 87% of invoices processed without human approval
- Override rate: 3.2%
- Approval latency (P95): 45 minutes
- Time saved per month: 120 hours (finance team)
- Passed internal security review on first submission
The company graduated to full autonomy for <$25K invoices after 120 days. The governance infrastructure they built for invoices now supports three additional agents (purchase order creation, vendor onboarding, expense report processing).
That's the 2-3x faster time-to-value on subsequent agents.
The regulatory timeline is compressing
EU AI Act enforcement begins December 2027. Penalties reach €15M or 3% of global revenue.
The Act requires:
- Human oversight for high-risk AI systems
- Documentation of training data and model decisions
- Risk management systems
- Accuracy and robustness testing
- Logging of automated decisions
Most enterprise agent deployments qualify as high-risk if they:
- Process financial transactions
- Make decisions affecting employment or contract terms
- Operate in regulated industries
The teams building governance architecture now are building defensible compliance positions. The teams retrofitting governance in late 2027 are building technical debt and regulatory risk.
Why this is an architectural moat
Companies that ship governance-first agent infrastructure establish competitive advantages:
Operational efficiency: Agents scale without linear headcount growth. Finance teams processing 10,000 invoices/month with the same team that handled 2,000.
Regulatory trust: When regulators audit your AI systems, you provide complete audit trails, documented approval workflows, and graduated autonomy validation. You pass.
Customer confidence: B2B customers increasingly ask "How do you govern your AI?" Companies with answers win deals.
Developer velocity: Once governance infrastructure exists, shipping additional agents takes weeks instead of months. The approval system, audit database, and role segregation are already built.
The CTO or CRO shipping autonomous systems without governance is shipping a liability. The one who invests upfront in approval workflows, audit trails, and graduated autonomy is shipping something defensible, scalable, and profitable.
What production-ready looks like
Production-ready agent deployment includes:
Technical infrastructure:
- Approval request/response API
- Policy engine for automated routing
- Audit database with immutable logs
- Role-based access controls
- Monitoring dashboard for governance KPIs
Process documentation:
- Risk classification framework
- Approval workflow diagrams
- Escalation procedures
- Policy update procedures
- Regulatory compliance attestation
Organizational readiness:
- Defined approver roles
- Trained approval reviewers
- Escalation contacts identified
- Security review completed
- Legal sign-off obtained
Most teams build 20% of this list. That's why 40% of pilots will be scrapped.
The teams shipping at scale build 100%.
Sources:
Want more on
Enterprise Architecture?
Add this topic to your Custom Digest. Drop your email to get our deepest insights on this exact topic.
Ready to fast-track your business?
We combine enterprise-level technical strategy with your existing business to solve complex blockers and accelerate your growth. Let's build something remarkable.
Partner With UsUp Next
Continue your journey into Enterprise Architecture.
How semantic content models automate SEO and content velocity
Learn how semantic content models eliminate engineering dependencies, automate SEO, and accelerate content deployment for enterprise marketing teams.
Why sovereign LLM deployments beat rented API model margins
Rented LLMs hide expensive costs in API fees and data transfer. Sovereign deployments cut vendor lock-in and deliver predictable margins.
Cut legacy technical debt with low-code agentic workflows
How to cut 40% of legacy system complexity in 18 months using low-code orchestration and AI agents.