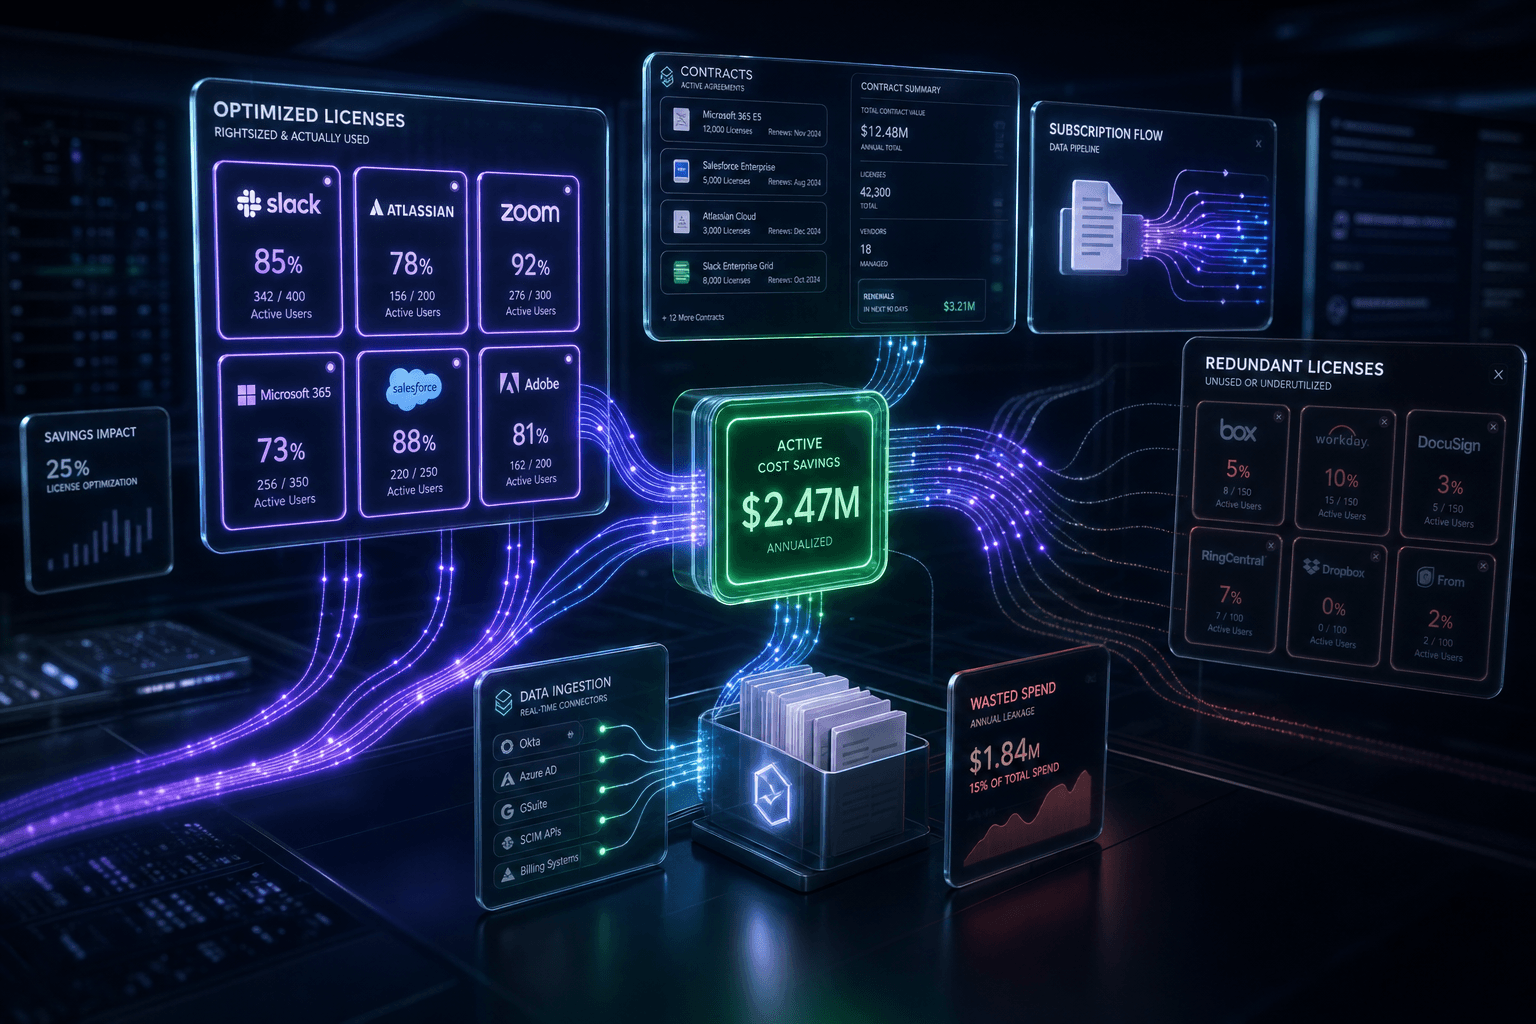
Eliminating phantom SaaS costs through licence compliance audits
How finance teams cut software spend by 15-25% through automated licence audits and usage monitoring.
Key Takeaways
- Phantom SaaS costs drain 15-25% of your software budget through unused licences and mis-provisioned seats.
- A unified software asset repository gives finance teams one source of truth for all licence agreements and usage.
- Automated utilisation monitoring flags underused subscriptions and triggers de-provisioning workflows before renewal cycles hit.
- Policy-driven procurement tied to real-time usage data stops unjustified licence purchases and protects operational margins.
SaaS sprawl is costing your business more than you think. Unused licences, redundant subscriptions, and mis-provisioned seats create phantom costs that quietly erode your margins. A licence compliance audit paired with automated asset management can reclaim 15-25% of your annual software spend.
Your finance team closes the quarter, reconciles the books, and discovers $47,000 in unaccounted SaaS spend. Nobody authorized it. Nobody's using half of it. Yet the charges keep hitting your accounts payable.
This isn't an anomaly. It's the norm for distributed enterprises running dozens of SaaS tools without a unified view of software consumption. Phantom SaaS costs—unused licences, over-provisioned seats, redundant subscriptions—represent 15-25% of total software spend in most mid-to-large organizations. That's capital bleeding out monthly while your CFO pushes for margin protection.
The root cause isn't careless spending. It's architectural. When software procurement operates independently from usage monitoring, and IT systems don't talk to finance systems, you create blind spots. Employees onboard, provision tools, then leave. Departments subscribe to overlapping solutions. Free trials convert to paid seats that nobody tracks. The result: a sprawling, ungoverned software estate that drains budget and exposes you to compliance risk.
Why traditional tracking fails
Most enterprises rely on spreadsheets, purchase order archives, or basic contract management systems to track SaaS subscriptions. This approach breaks down at scale for three reasons:
Decentralized procurement: Business units buy tools directly using corporate cards, bypassing central IT and finance approval. Your visibility ends at the invoice, not at actual usage.
Static data: Spreadsheets capture what you bought, not what you're using. A 100-seat licence might serve 32 active users. Without real-time utilisation data, you're flying blind.
No enforcement mechanism: Even when finance identifies waste, there's no automated way to de-provision unused seats or block renewals. Manual intervention is slow, inconsistent, and often ignored.
The financial impact compounds. You overpay on renewals, miss opportunities to downgrade tiers, and lack the data to negotiate vendor contracts. Worse, you face audit risk. Software vendors are increasingly aggressive with compliance audits, and undocumented or mis-provisioned licences trigger penalties that dwarf the original subscription cost.
Centralizing control without adding friction
Software asset management (SAM) isn't a procurement checkbox. It's an architectural pattern that connects financial oversight to operational reality. The goal: establish a single source of truth for every software asset, from purchase through de-provisioning, with automated workflows that prevent leakage without slowing down the business.
Here's the three-layer architecture:
Unified software asset repository
Build or integrate a centralized repository that consolidates all software purchase data, contracts, and licence agreements. This isn't a new silo—it extends your existing ERP or finance system to include:
- Contract metadata: Vendor, SKU, licence type (per-user, per-device, concurrent), tier, renewal date, termination clauses.
- Purchase history: Who bought it, which cost center, approval chain, payment method.
- Entitlements: Total seats purchased, allocation by department or user group.
The repository must be immutable (audit-grade) and API-accessible so downstream systems can query licence status in real time. Integration with identity providers (Active Directory, Okta, Azure AD) ensures you know who has access to what.
Automated utilisation monitoring
Purchase data tells you what you own. Utilisation data tells you what you're actually using. Implement automated monitoring that tracks:
- Login frequency: Last login date, login count over trailing 30/60/90 days.
- Feature engagement: Which modules or features are accessed (if the SaaS vendor exposes this via API or usage logs).
- Device/location: Multi-device logins, geographic distribution, which can flag shared credentials or non-compliant usage.
Feed this data into a dashboard that flags:
- Inactive licences: No login in 60+ days.
- Under-utilised tiers: Paying for premium features nobody uses.
- Redundant tools: Multiple products serving the same function across departments.
The key architectural decision: build this monitoring layer as a microservice or middleware that polls SaaS APIs (or ingests SIEM/log data) and writes to your asset repository. Don't rely on manual audits or vendor-provided reports, which are often delayed or incomplete.
Policy-driven provisioning and renewal
Once you have real-time utilisation data, enforce policies that prevent waste:
- Automated de-provisioning: If a licence is inactive for 60 days, trigger a notification to the user and manager. If still inactive after 90 days, automatically de-provision and reallocate the seat.
- Approval workflows for new purchases: Route all SaaS procurement through a lightweight approval process that checks for existing licences or redundant tools before issuing new subscriptions.
- Renewal gating: 90 days before renewal, generate a utilisation report. If usage is below threshold (e.g., <50% of seats active), flag for review and negotiation or cancellation.
These policies must be codified in your workflow automation platform, not buried in a procurement manual. Use your ERP's workflow engine, a dedicated SAM platform, or a custom orchestration layer to enforce them consistently.
The execution roadmap
Implementing this architecture doesn't require ripping out existing systems. Here's a phased approach that minimizes disruption:
Phase 1 (Weeks 1-4): Discovery and data consolidation
- Audit all current SaaS subscriptions. Pull data from AP invoices, credit card statements, ERP purchase orders, and direct vendor queries.
- Identify shadow IT by surveying department heads and scanning SSO logs.
- Consolidate into a master spreadsheet or staging database (this becomes your initial repository).
Phase 2 (Weeks 5-8): Repository build and integration
- Extend your ERP or deploy a SAM platform (e.g., Flexera, Snow, Zylo, or build custom if you have the engineering capacity).
- Integrate with identity providers and payment systems to automate data ingestion.
- Set up API connectors to major SaaS vendors for automated licence and usage data pulls.
Phase 3 (Weeks 9-12): Monitoring and alerting
- Deploy utilisation monitoring scripts or middleware to poll SaaS APIs.
- Build a dashboard for finance and IT teams showing real-time licence status, utilisation rates, and cost projections.
- Configure alerts for inactive licences, over-provisioning, and upcoming renewals.
Phase 4 (Weeks 13+): Policy enforcement and continuous improvement
- Roll out automated de-provisioning workflows for inactive users.
- Implement approval gates for new SaaS purchases.
- Conduct quarterly reviews to refine thresholds, identify new redundancies, and renegotiate vendor contracts based on usage data.
Measurable outcomes and ROI
This approach delivers quantifiable financial and operational benefits:
Cost reduction: Clients typically reduce SaaS spend by 15-25% within the first year by eliminating unused licences, downgrading over-provisioned tiers, and consolidating redundant tools. For a $2M annual SaaS budget, that's $300-500K in immediate savings.
Audit readiness: Centralized, immutable records of every licence and its usage history mean you can respond to vendor audits in hours, not weeks, and defend against unjustified penalty claims.
Budget predictability: Real-time utilisation data lets you forecast renewals and new purchases with accuracy, reducing budget variance and enabling better capital allocation.
Freed capacity: Finance and IT teams spend 40-60% less time on manual licence reconciliation and firefighting, redirecting that effort toward strategic projects.
The compliance and risk dimension
Beyond cost, ungoverned SaaS creates compliance and security risks:
- Licence violations: Using more seats than purchased, or using software outside contractual scope, exposes you to penalties that can reach 3-5x the original licence cost.
- Data sprawl: Unused accounts with access to sensitive data create attack surface and violate data residency or retention policies.
- Contract lock-in: Auto-renewing subscriptions that go unmonitored can trap you in unfavorable terms or prevent you from switching to better alternatives.
A SAM framework mitigates these risks by enforcing visibility and control at every stage of the software lifecycle.
Why finance and IT must co-own this
SAM isn't a finance problem or an IT problem—it's a shared operational imperative. Finance owns the budget and contract terms. IT owns provisioning and access control. Procurement owns vendor relationships. Without tight coordination, gaps emerge.
Establish a cross-functional SAM steering committee with representation from finance, IT, procurement, and legal. Meet quarterly to review utilisation data, update policies, and prioritize vendor negotiations. Make SAM a standing agenda item in budget reviews and operational planning.
Building this without adding technical debt
The biggest risk in SAM implementations is building a brittle, point-to-point integration web that becomes unmaintainable. Avoid this by:
- Using APIs and webhooks: Don't scrape vendor portals or rely on manual exports. Insist on API access in your SaaS contracts.
- Keeping the data model simple: Resist the urge to track every possible attribute. Focus on the minimum viable schema: vendor, product, licence type, seats, cost, utilisation.
- Version controlling policies: Store provisioning and renewal policies as code in a version control system so changes are auditable and reversible.
- Choosing composable tools: If buying a SAM platform, ensure it integrates cleanly with your ERP and identity systems. If building custom, use lightweight microservices that can be replaced without rearchitecting the entire stack.
What finance leaders should demand from IT
If you're a CFO or finance leader pushing for SAM, here's what to ask your CTO:
- Can you give me a real-time dashboard showing every SaaS subscription, its utilisation rate, and projected annual cost?
- Can we automate de-provisioning for users who've been inactive for 90 days?
- Can we block new SaaS purchases unless they go through an approval workflow that checks for redundancy?
- Can we generate an audit-ready report of all software licences and their usage history in under an hour?
If the answer to any of these is no, you have an architectural gap that's costing you money every month.
The path forward
Phantom SaaS costs aren't inevitable. They're the result of decoupled systems and missing feedback loops between finance, IT, and procurement. By building a unified SAM framework—centralized repository, automated monitoring, policy-driven workflows—you close those gaps and turn software spend from a black box into a managed, optimized asset class.
The ROI is immediate. The risk reduction is measurable. The operational clarity pays dividends across the enterprise. Start with discovery, consolidate your data, and build the architecture that gives you control.
Want more on
Business Operations?
Add this topic to your Custom Digest. Drop your email to get our deepest insights on this exact topic.
Ready to fast-track your business?
We combine enterprise-level technical strategy with your existing business to solve complex blockers and accelerate your growth. Let's build something remarkable.
Partner With UsUp Next
Continue your journey into Business Operations.
Why operational risk starts with unverified data integrity
Learn why unverified data integrity creates cascading operational failures and how to architect proactive validation into your enterprise systems.
Reducing integration debt opex with event-driven data fabrics
How event-driven integration cuts operational costs by eliminating technical debt and reducing manual IT overhead.
Dismantling enterprise data silos with centralised knowledge graphs
How a unified knowledge graph cuts IT integration costs and powers real-time decisions across fragmented enterprise systems.